



































































































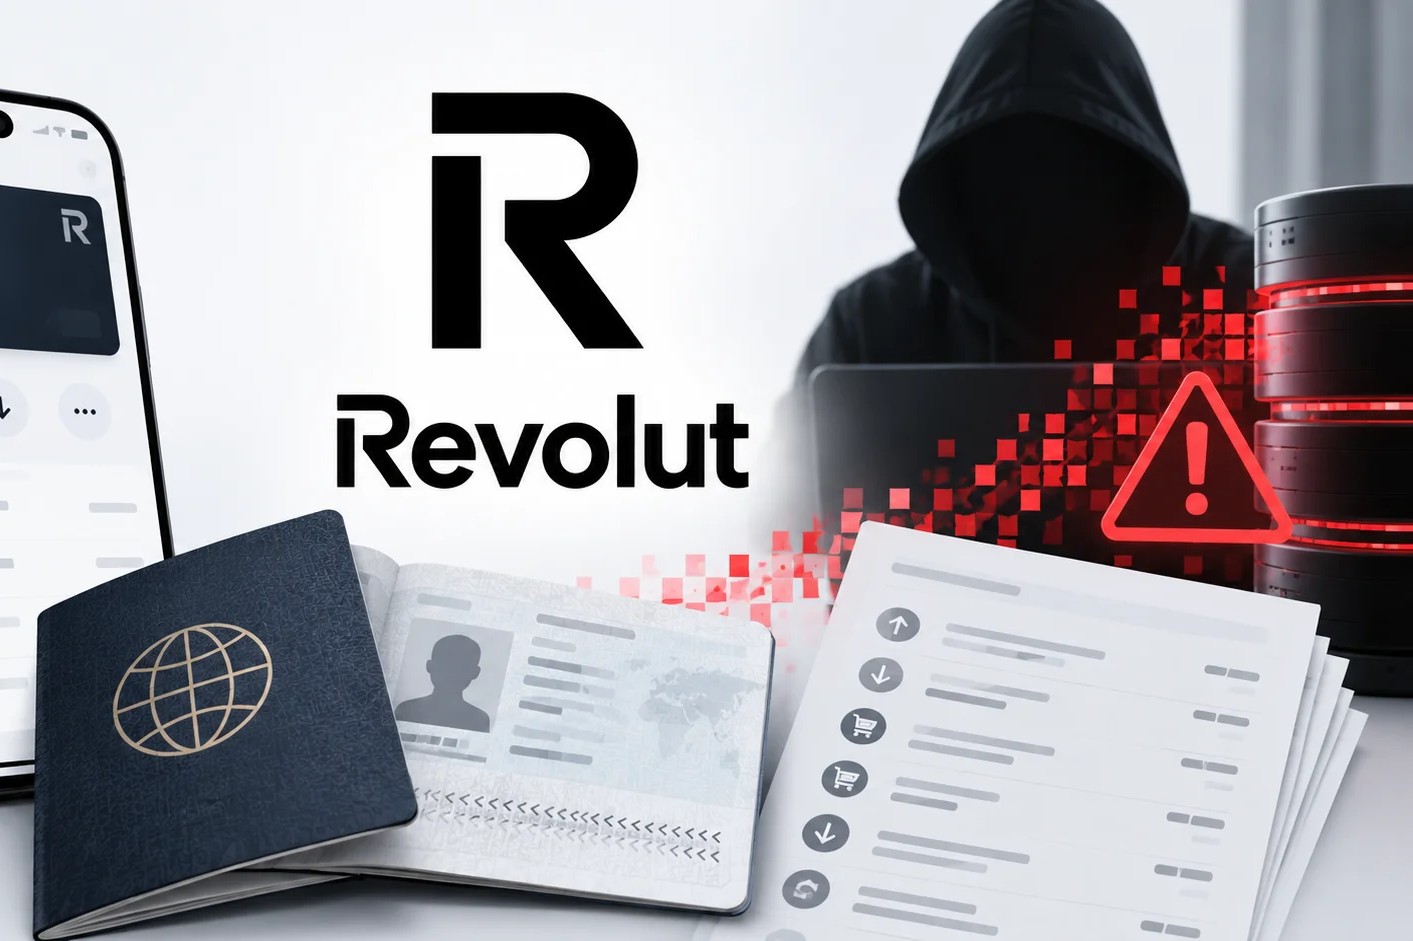
The hackers claiming responsibility for Revolut’s recent customer data breach are demanding $3 million in Monero and threatening to sell sensitive information belonging to hundreds of customers if the payment isn’t made. The group, calling itself “iamnotavillain,” publicly demanded 6,000 XMR and reportedly gave Revolut 24 hours to comply. Revolut says it has not received any direct communication or ransom demand from the group.
Hackers Demand 6,000 XMR
The attackers published their ultimatum alongside a countdown clock, demanding 6,000 Monero worth approximately $3 million.
The group threatened to sell the stolen information to other criminal organizations if Revolut refused to pay. Monero (XMR) is a privacy-focused cryptocurrency designed to obscure details including transaction amounts, senders and recipients.
Nearly 700 Revolut Customers Reportedly Affected
The breach is understood to involve approximately 680 customer accounts, although Revolut has publicly described the affected group only as a limited number of customers.
Information reportedly exposed includes:
- Passports and driver’s licenses
- KYC verification photos
- Home addresses and contact information
- Account and transaction histories
- Crypto deposits and withdrawals
Revolut says its core infrastructure, databases and customer accounts were not hacked and customer funds remain unaffected.
Crypto Whales Were Allegedly Targeted
The attackers claim the victims weren’t selected randomly.
According to the group, blockchain analysis was used to identify Revolut customers with significant cryptocurrency holdings before fraudulent requests were submitted seeking information about those specific individuals.
That detail creates an additional security concern because leaked identity documents, transaction histories and home addresses could potentially connect high-value onchain activity with real-world identities.
Hackers Posed as Government Officials
The attackers didn’t reportedly break directly into Revolut’s banking infrastructure.
Instead, Revolut previously confirmed that an unauthorized party used an email address associated with a legitimate government agency domain to submit fraudulent information requests. Revolut responded to the requests before discovering they were fraudulent.
The attackers separately claim they compromised an Italian government email system and posed as law enforcement over several months. That account has been reported by the Financial Times but hasn’t been independently confirmed by Revolut.
After discovering the scheme, Revolut says it blocked the address and contacted the relevant government agency, law enforcement and regulators.
Revolut Says It Hasn’t Received the Ransom Demand
Despite the public ultimatum, Revolut told Reuters that it hadn’t received direct contact or a ransom demand from the individuals claiming responsibility as of September 16.
That means the $3 million demand currently represents a public threat from the alleged attackers rather than an acknowledged private negotiation between Revolut and the group.
Revolut Breach Becomes an Extortion Case
What began as a fraudulent government-data request has now escalated into an alleged multimillion-dollar extortion attempt.
The combination of KYC documents, physical addresses and crypto transaction histories is particularly concerning for cryptocurrency holders because blockchain activity that was previously pseudonymous could potentially be connected with specific individuals.
With the attackers now demanding 6,000 XMR and threatening to sell the information, the Revolut incident has evolved from a serious privacy breach into a broader security threat for the customers whose identities and crypto activity were exposed.
- Sam Bankman-Fried Officially Requests Presidential Pardon From Trump
- Sam Bankman Fried Withdraws New Trial Motion While Denying Ghostwriting Allegations
- John Gotti’s Grandson Sentenced to Prison in $1.1 Million COVID Fraud and Crypto Scheme
- US Soldier Accused of Using Classified Intel for Polymarket Trades Was Blocked by Kalshi
- Polish Prime Minister Accuses Crypto Firm of Russian Mafia Ties and Political Influence
- Chinese Billionaire Guo Wengui Sentenced to 30 Years in Prison for $1 Billion Crypto and Investment Fraud