




































































































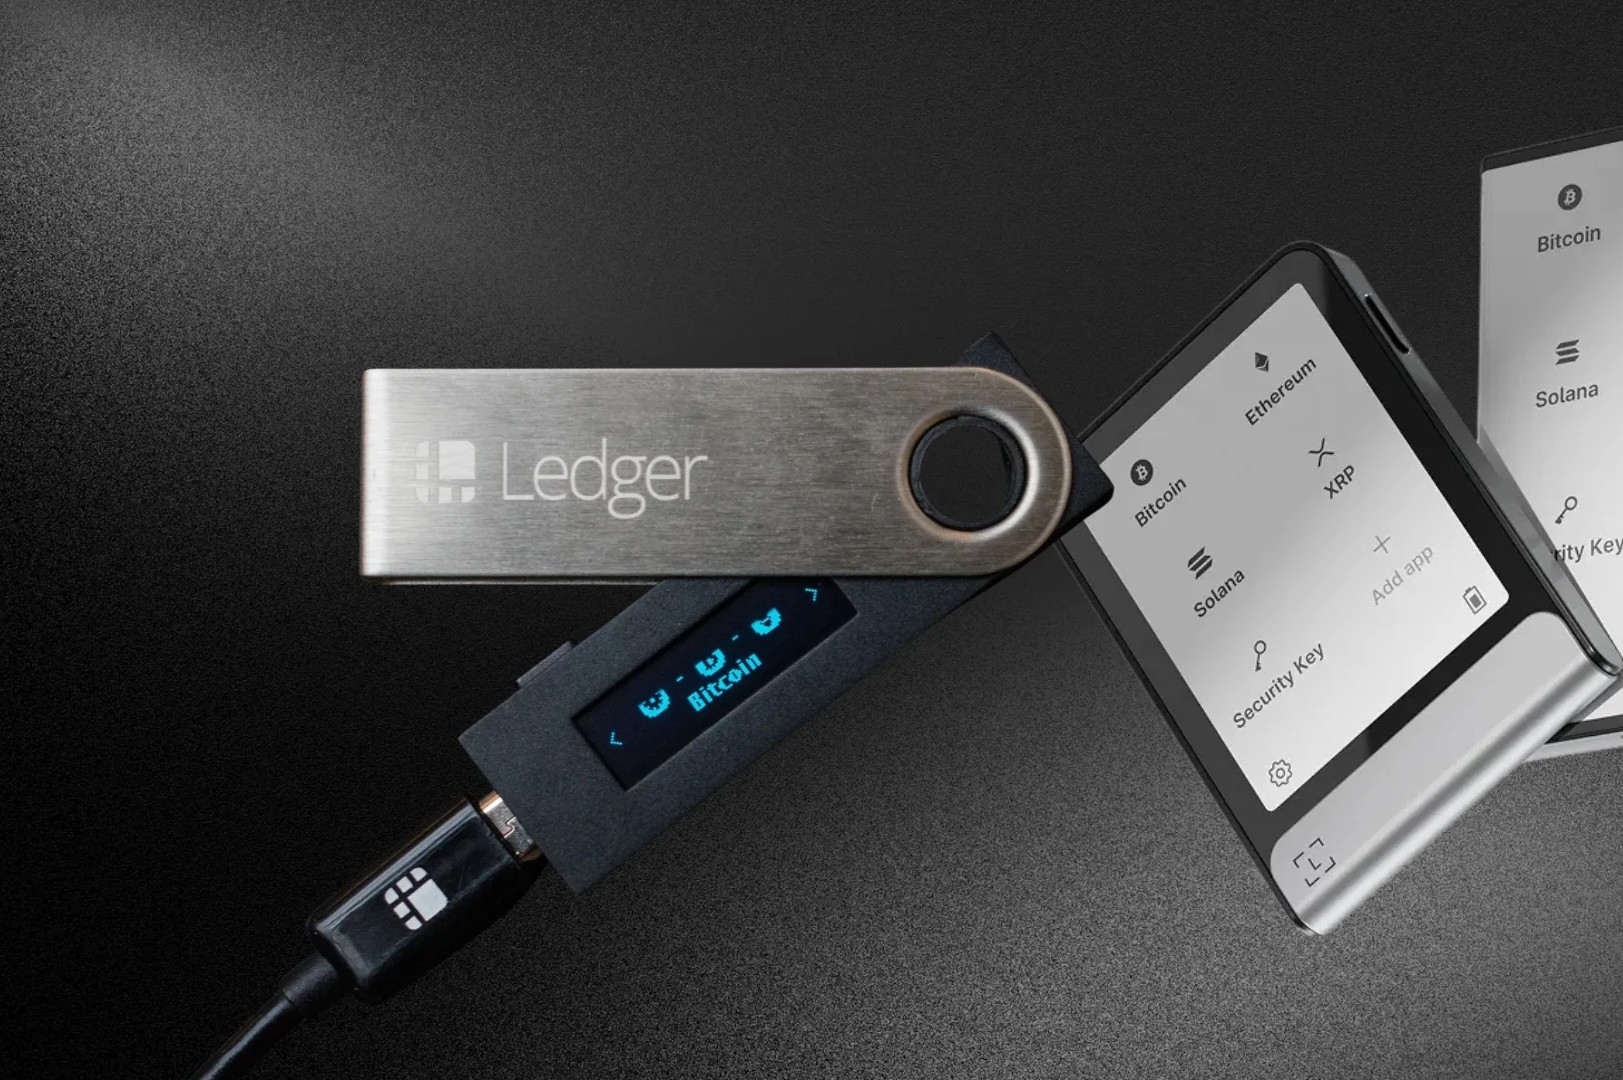
Cryptocurrency hardware wallet manufacturer Ledger has confirmed that compromised devices have been discovered in Berlin, Germany, as its investigation into a sophisticated supply-chain attack expands beyond Southeast Asia. In a November 18, 2026 update, Ledger revealed that investigators are also examining two suspected tampered wallets in Dubai, United Arab Emirates. The developments are connected to an ongoing investigation involving approximately $87 million in suspected cryptocurrency thefts, where criminals allegedly installed hidden electronic components inside genuine Ledger devices to steal users’ recovery phrases.
Ledger Wallet Attack Spreads Beyond Southeast Asia
The investigation began in October 2026, after customers who purchased Ledger wallets from third-party reseller CryptoBilis reported that their cryptocurrency holdings had been stolen.
Blockchain investigators subsequently identified approximately $87 million in suspected stolen assets across hundreds of wallets involving Bitcoin, Ethereum and TRON.
Initially, the confirmed cases were concentrated in Southeast Asia. However, Ledger’s latest investigation identified additional compromised devices in other regions.
The company’s findings include:
Berlin, Germany: Several confirmed tampered wallets. Customers who purchased Ledger devices in Berlin since January 2026 are advised to contact Ledger Support.
Dubai, UAE: Two suspected compromised devices are under investigation, with reports linking purchases to a Virgin Megastore location.
Southeast Asia: Investigators identified an additional affected Ledger Nano Gen5 among previously suspended resellers.
Ledger warned that more compromised devices could emerge as the investigation continues.
Hackers Installed Hidden Hardware to Steal Recovery Phrases
Unlike traditional cryptocurrency hacks targeting software vulnerabilities, this attack involved physically modifying genuine hardware wallets before customers received them.
Criminals allegedly installed concealed electronic components designed to capture users’ 24-word recovery phrases during the initial setup process.
A recovery phrase serves as the master key to a cryptocurrency wallet. Anyone possessing it can potentially access and transfer the wallet’s funds without authorization.
Ledger emphasized that its secure chip, operating system and internal infrastructure were not compromised.
The company also stated that investigators have found no confirmed cases involving devices purchased directly from Ledger’s official website.
Instead, the attack appears to have targeted third-party distribution channels.
Ledger Offers Security Inspections and Warns Customers
Ledger’s internal security team, Donjon, continues examining suspicious devices while working with distributors and law enforcement.
The company is temporarily offering physical inspections, including X-ray examinations, at its manufacturing facility in Vierzon, France.
Customers concerned about compromised devices should:
Stop using the suspicious wallet and avoid entering recovery phrases.
Transfer funds to a newly created wallet using a device purchased directly from Ledger’s official website.
Generate a completely new recovery phrase rather than reusing the original phrase or passphrase.
Contact official Ledger Support and report suspected thefts to local authorities.
Ledger also reminded customers that legitimate support representatives will never request their recovery phrases.
Hardware Wallet Security Faces Growing Supply-Chain Threats
The incident highlights a growing cybersecurity concern for cryptocurrency investors: hardware wallets can be compromised before they reach customers, even when the manufacturer’s underlying technology remains secure.
The investigation comes as competing wallet manufacturer Trezor disclosed a separate third-party shipping provider breach potentially exposing information associated with approximately 27,000 orders.
Although the incidents involve different attack methods, both demonstrate how criminals are increasingly targeting external suppliers and distributors.
For the broader Web3 industry, Ledger’s expanding investigation reinforces the importance of securing the entire hardware wallet supply chain. While cold storage remains an important tool for protecting digital assets, purchasing devices through trusted channels and safeguarding recovery phrases are essential to preventing cryptocurrency theft.
- Telefónica Partners With Helium to Roll Out Mobile Hotspots in Mexico
- Bybit, Binance, and Bitget Cancel Tokenized SpaceX IPO Allocations After Demand Overwhelms Supply
- Solo Bitcoin Miner Beats 1-in-180-Million Odds to Land $265,000 Block
- Jack Dorsey Evokes Bitcoin Ethos with New Decentralized Messaging App Bitchat
- Rumble Joins With Tether to Introduce Bitcoin Tipping For its 51 Million Users
- Ledger Says Ethereum Wallet Flaw Was Patched Before Public Security Warning